

Network Security Through Data Analysis
Building Situational Awareness
Autori
Viac o knihe
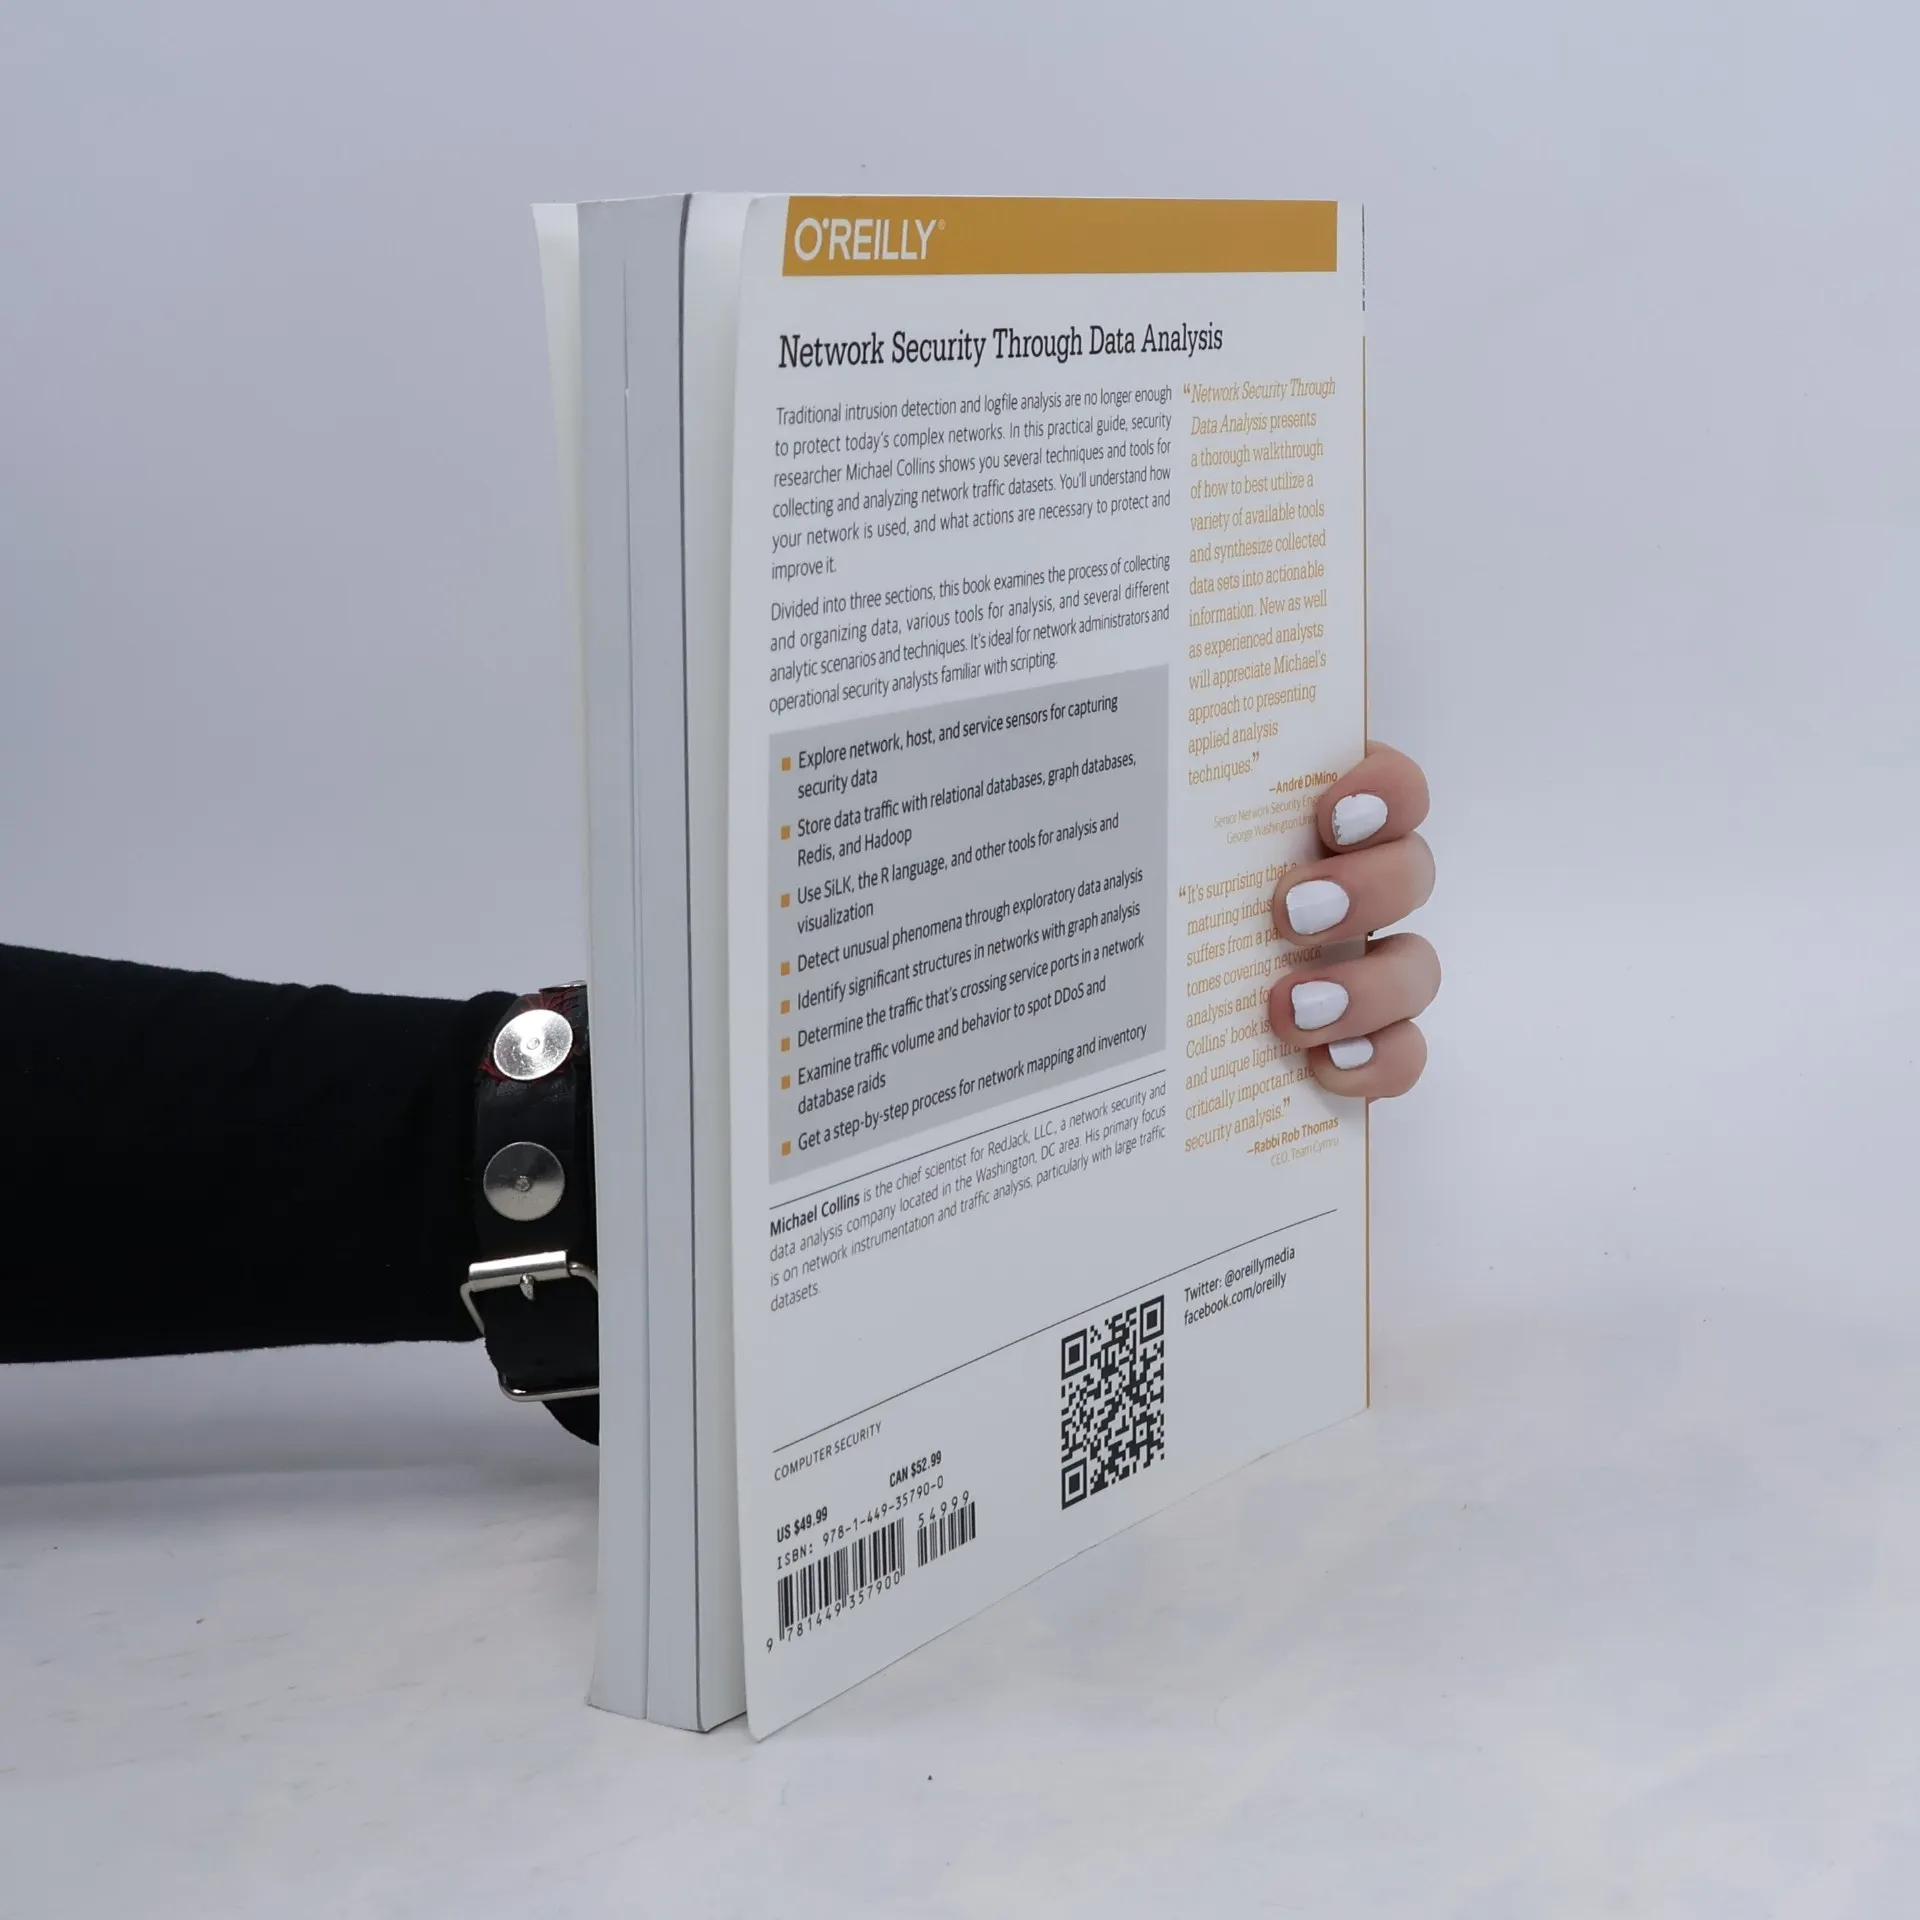
System and network administrators have traditionally monitored their systems through general tools such as intrusion detection and logfile analysis. But modern, complex networks, suffering from more and more sophisticated attacks, deserve more analytical tools. Michael Collins, a leading researcher in security, introduces the techniques needed in this book and highlights some of the computing tools that will help catch problems. The book is divided into three large sections: data collection, analysis, and taking action. These can be iterative, as each discovery alerts the administrator to data that should be collected. Several forms of analysis and visualization are covered. Topics include: What data to capture on your systems Data fusion Structures and storage systems for data Using R, SiLK, and Python for analysis Visualization and exploratory data analysis Graph analysis Network mapping Address forensics: determining where traffic originates Handling malware
Nákup knihy
Network Security Through Data Analysis, Edgar Collins
- Jazyk

- Rok vydania
- 2014
- Väzba
- (mäkká)
Doručenie
Platobné metódy
Nikto zatiaľ neohodnotil.
- Titul
- Network Security Through Data Analysis
- Podtitul
- Building Situational Awareness
- Jazyk
- anglicky
- Autori
- Edgar Collins
- Vydavateľ
- O'Reilly
- Rok vydania
- 2014
- Väzba
- mäkká
- Počet strán
- 348
- ISBN10
- 1449357903
- ISBN13
- 9781449357900
- Série
- Štítky
- Príručky a návody, USA, Technológia, Odborná literatúra, Komunikácia, Bezpečnosť, Analýza dát, Počítačové siete, Veľké dáta, Vizualizácia, Hedvábie
- Anotácia
- System and network administrators have traditionally monitored their systems through general tools such as intrusion detection and logfile analysis. But modern, complex networks, suffering from more and more sophisticated attacks, deserve more analytical tools. Michael Collins, a leading researcher in security, introduces the techniques needed in this book and highlights some of the computing tools that will help catch problems. The book is divided into three large sections: data collection, analysis, and taking action. These can be iterative, as each discovery alerts the administrator to data that should be collected. Several forms of analysis and visualization are covered. Topics include: What data to capture on your systems Data fusion Structures and storage systems for data Using R, SiLK, and Python for analysis Visualization and exploratory data analysis Graph analysis Network mapping Address forensics: determining where traffic originates Handling malware