
Presne táto pôjde do košíka
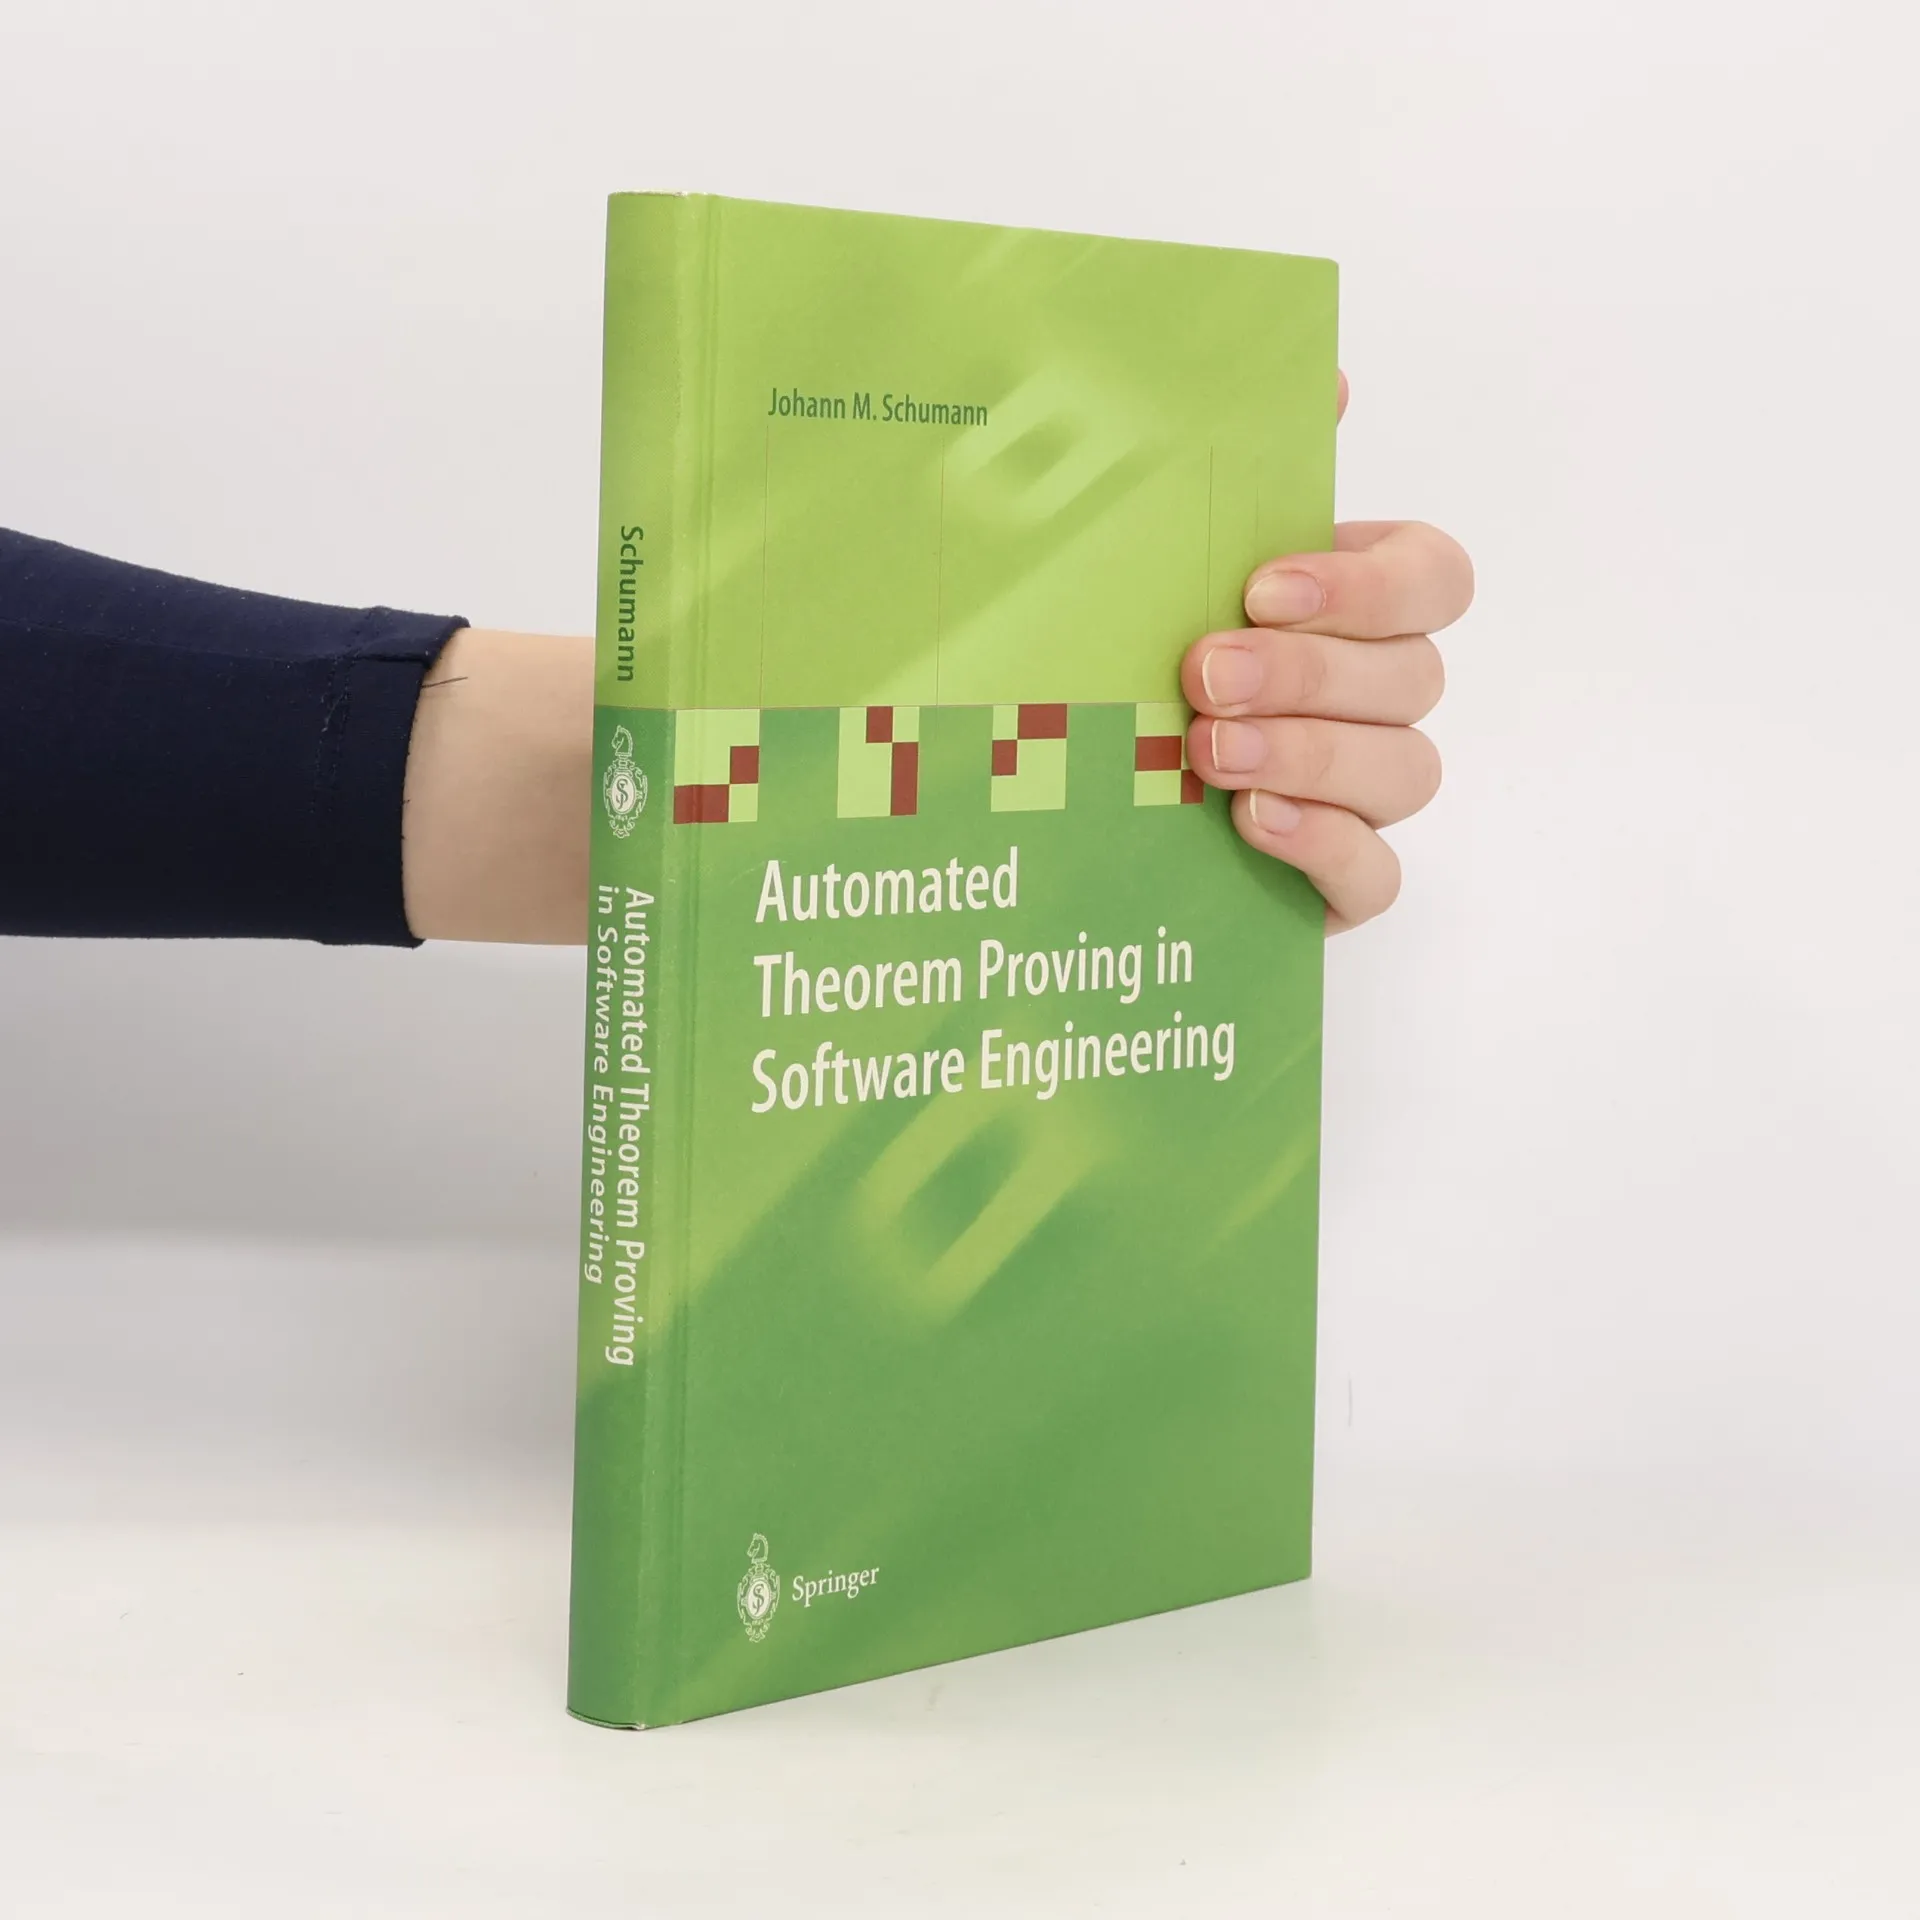
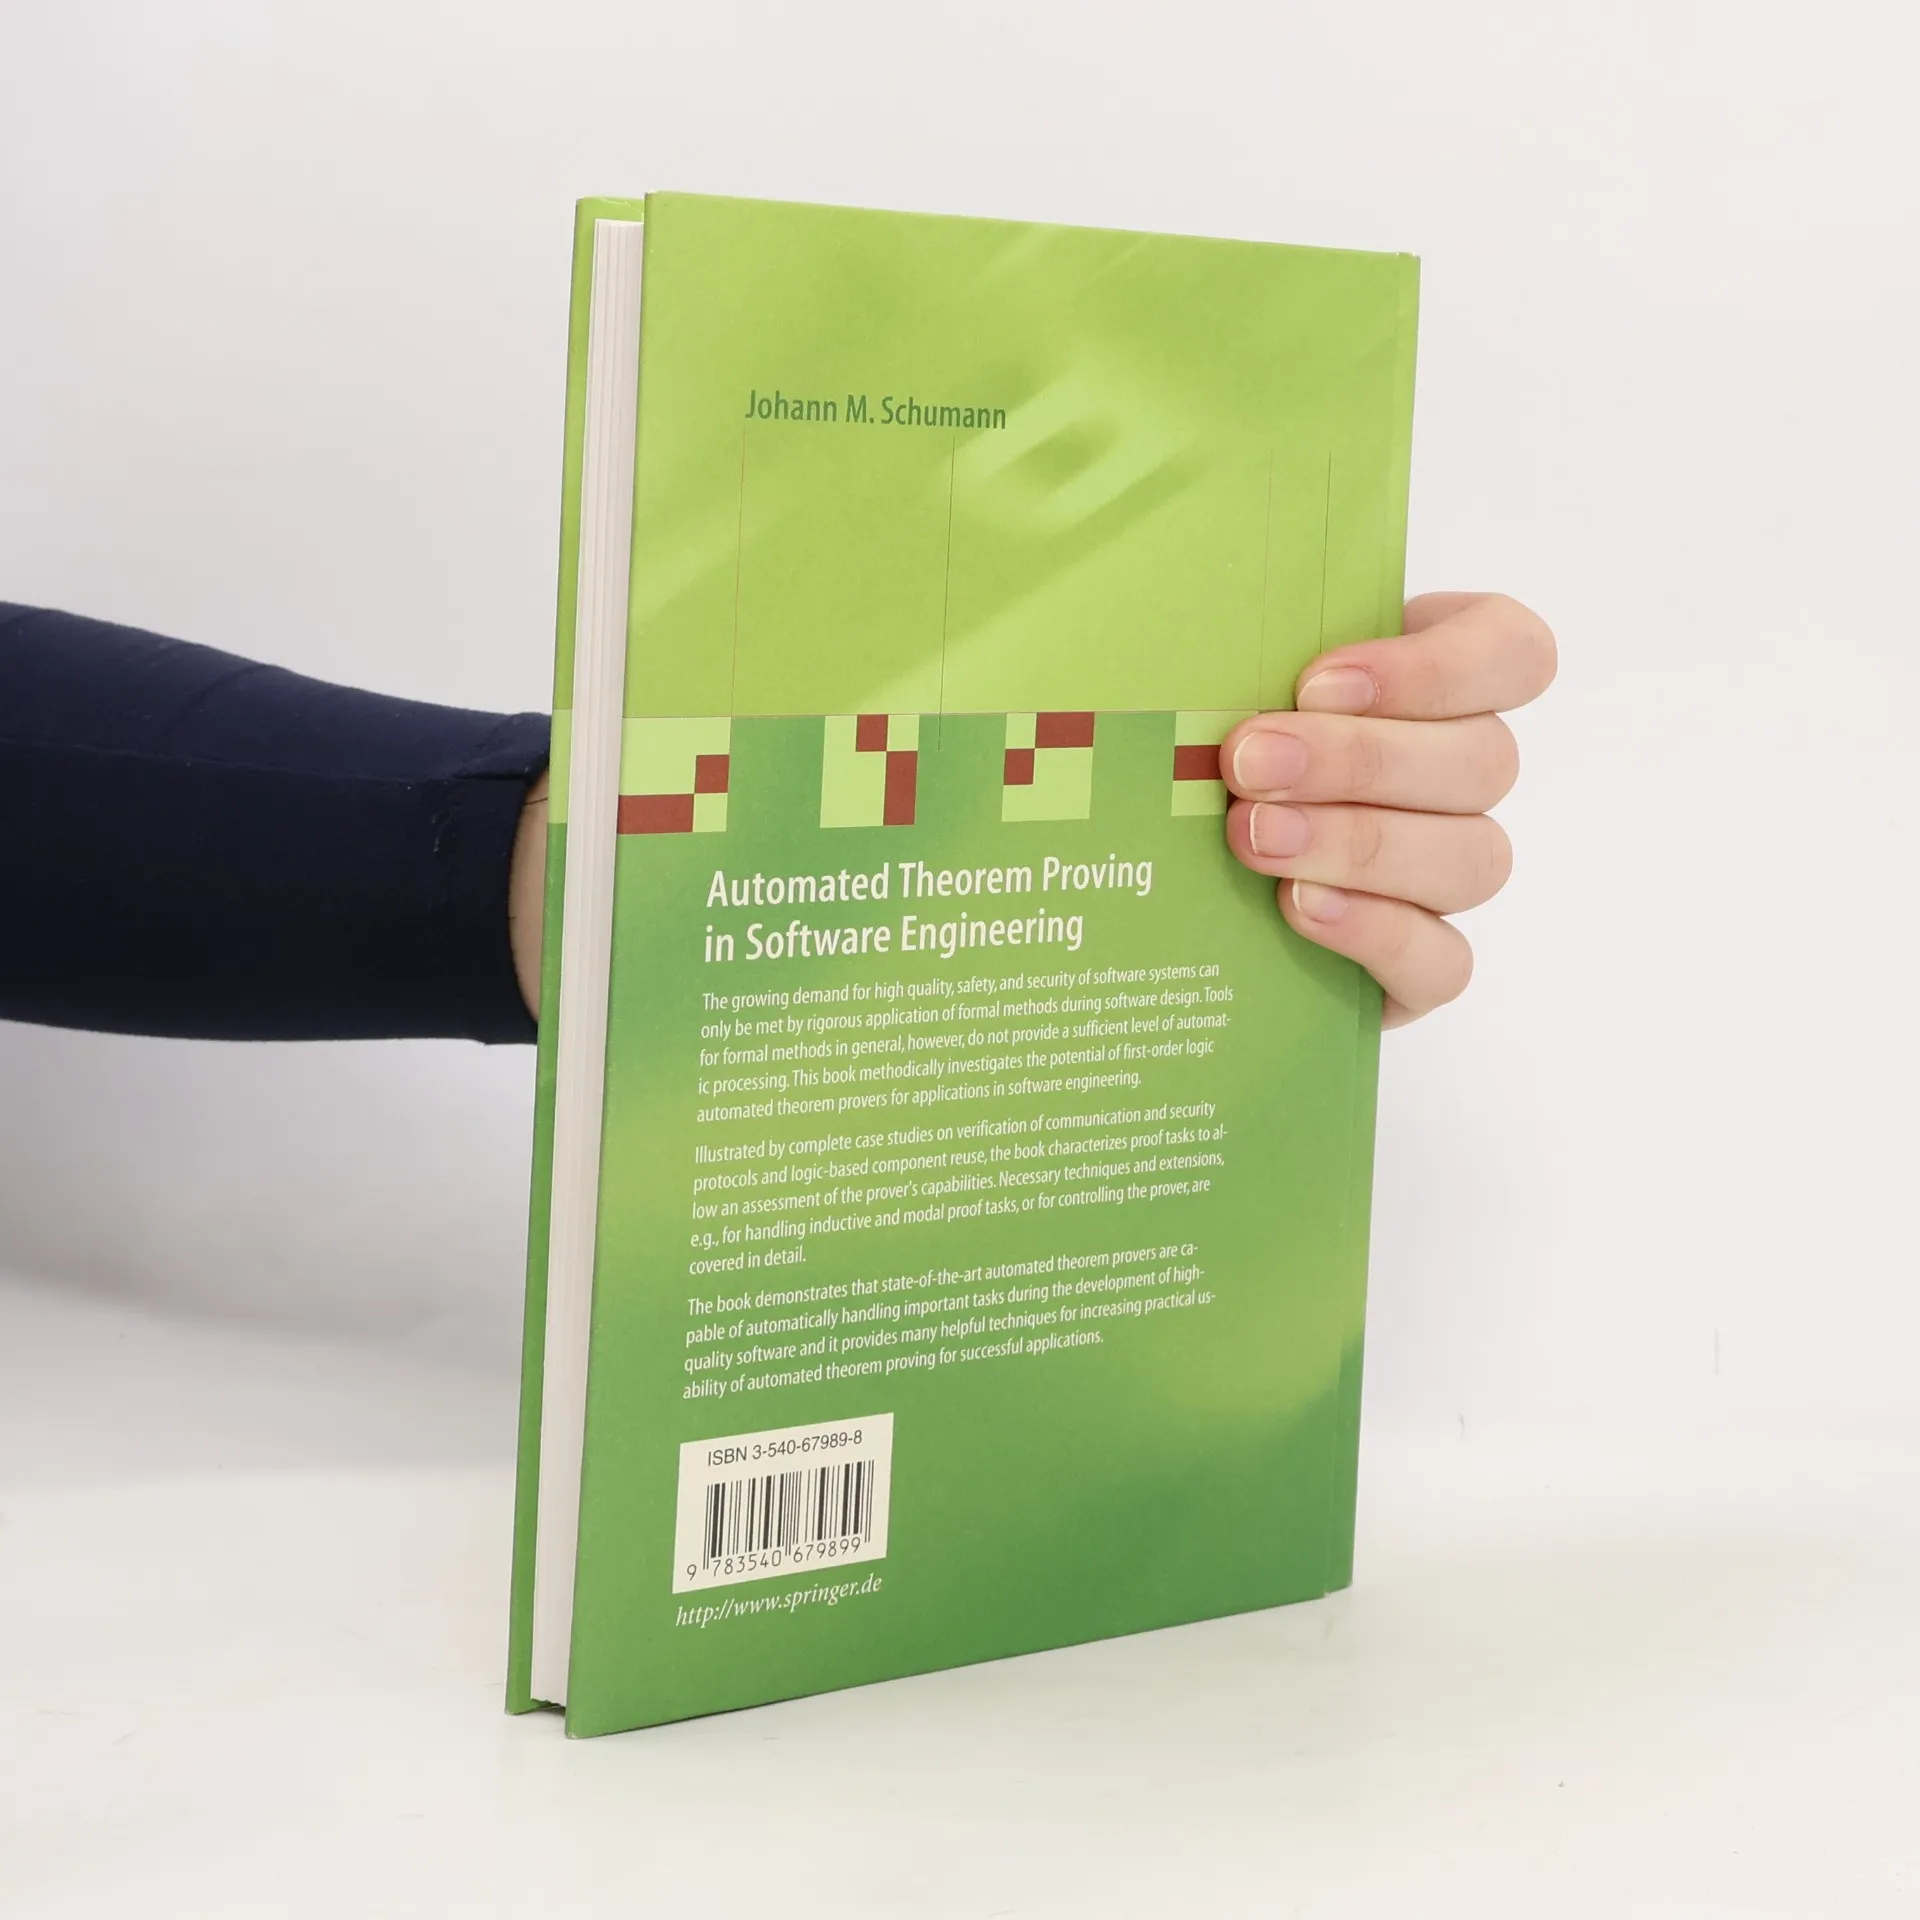
Automated Theorem Proving in Software Engineering
Parametre
- 228 stránok
- 8 hodin čítania
Viac o knihe
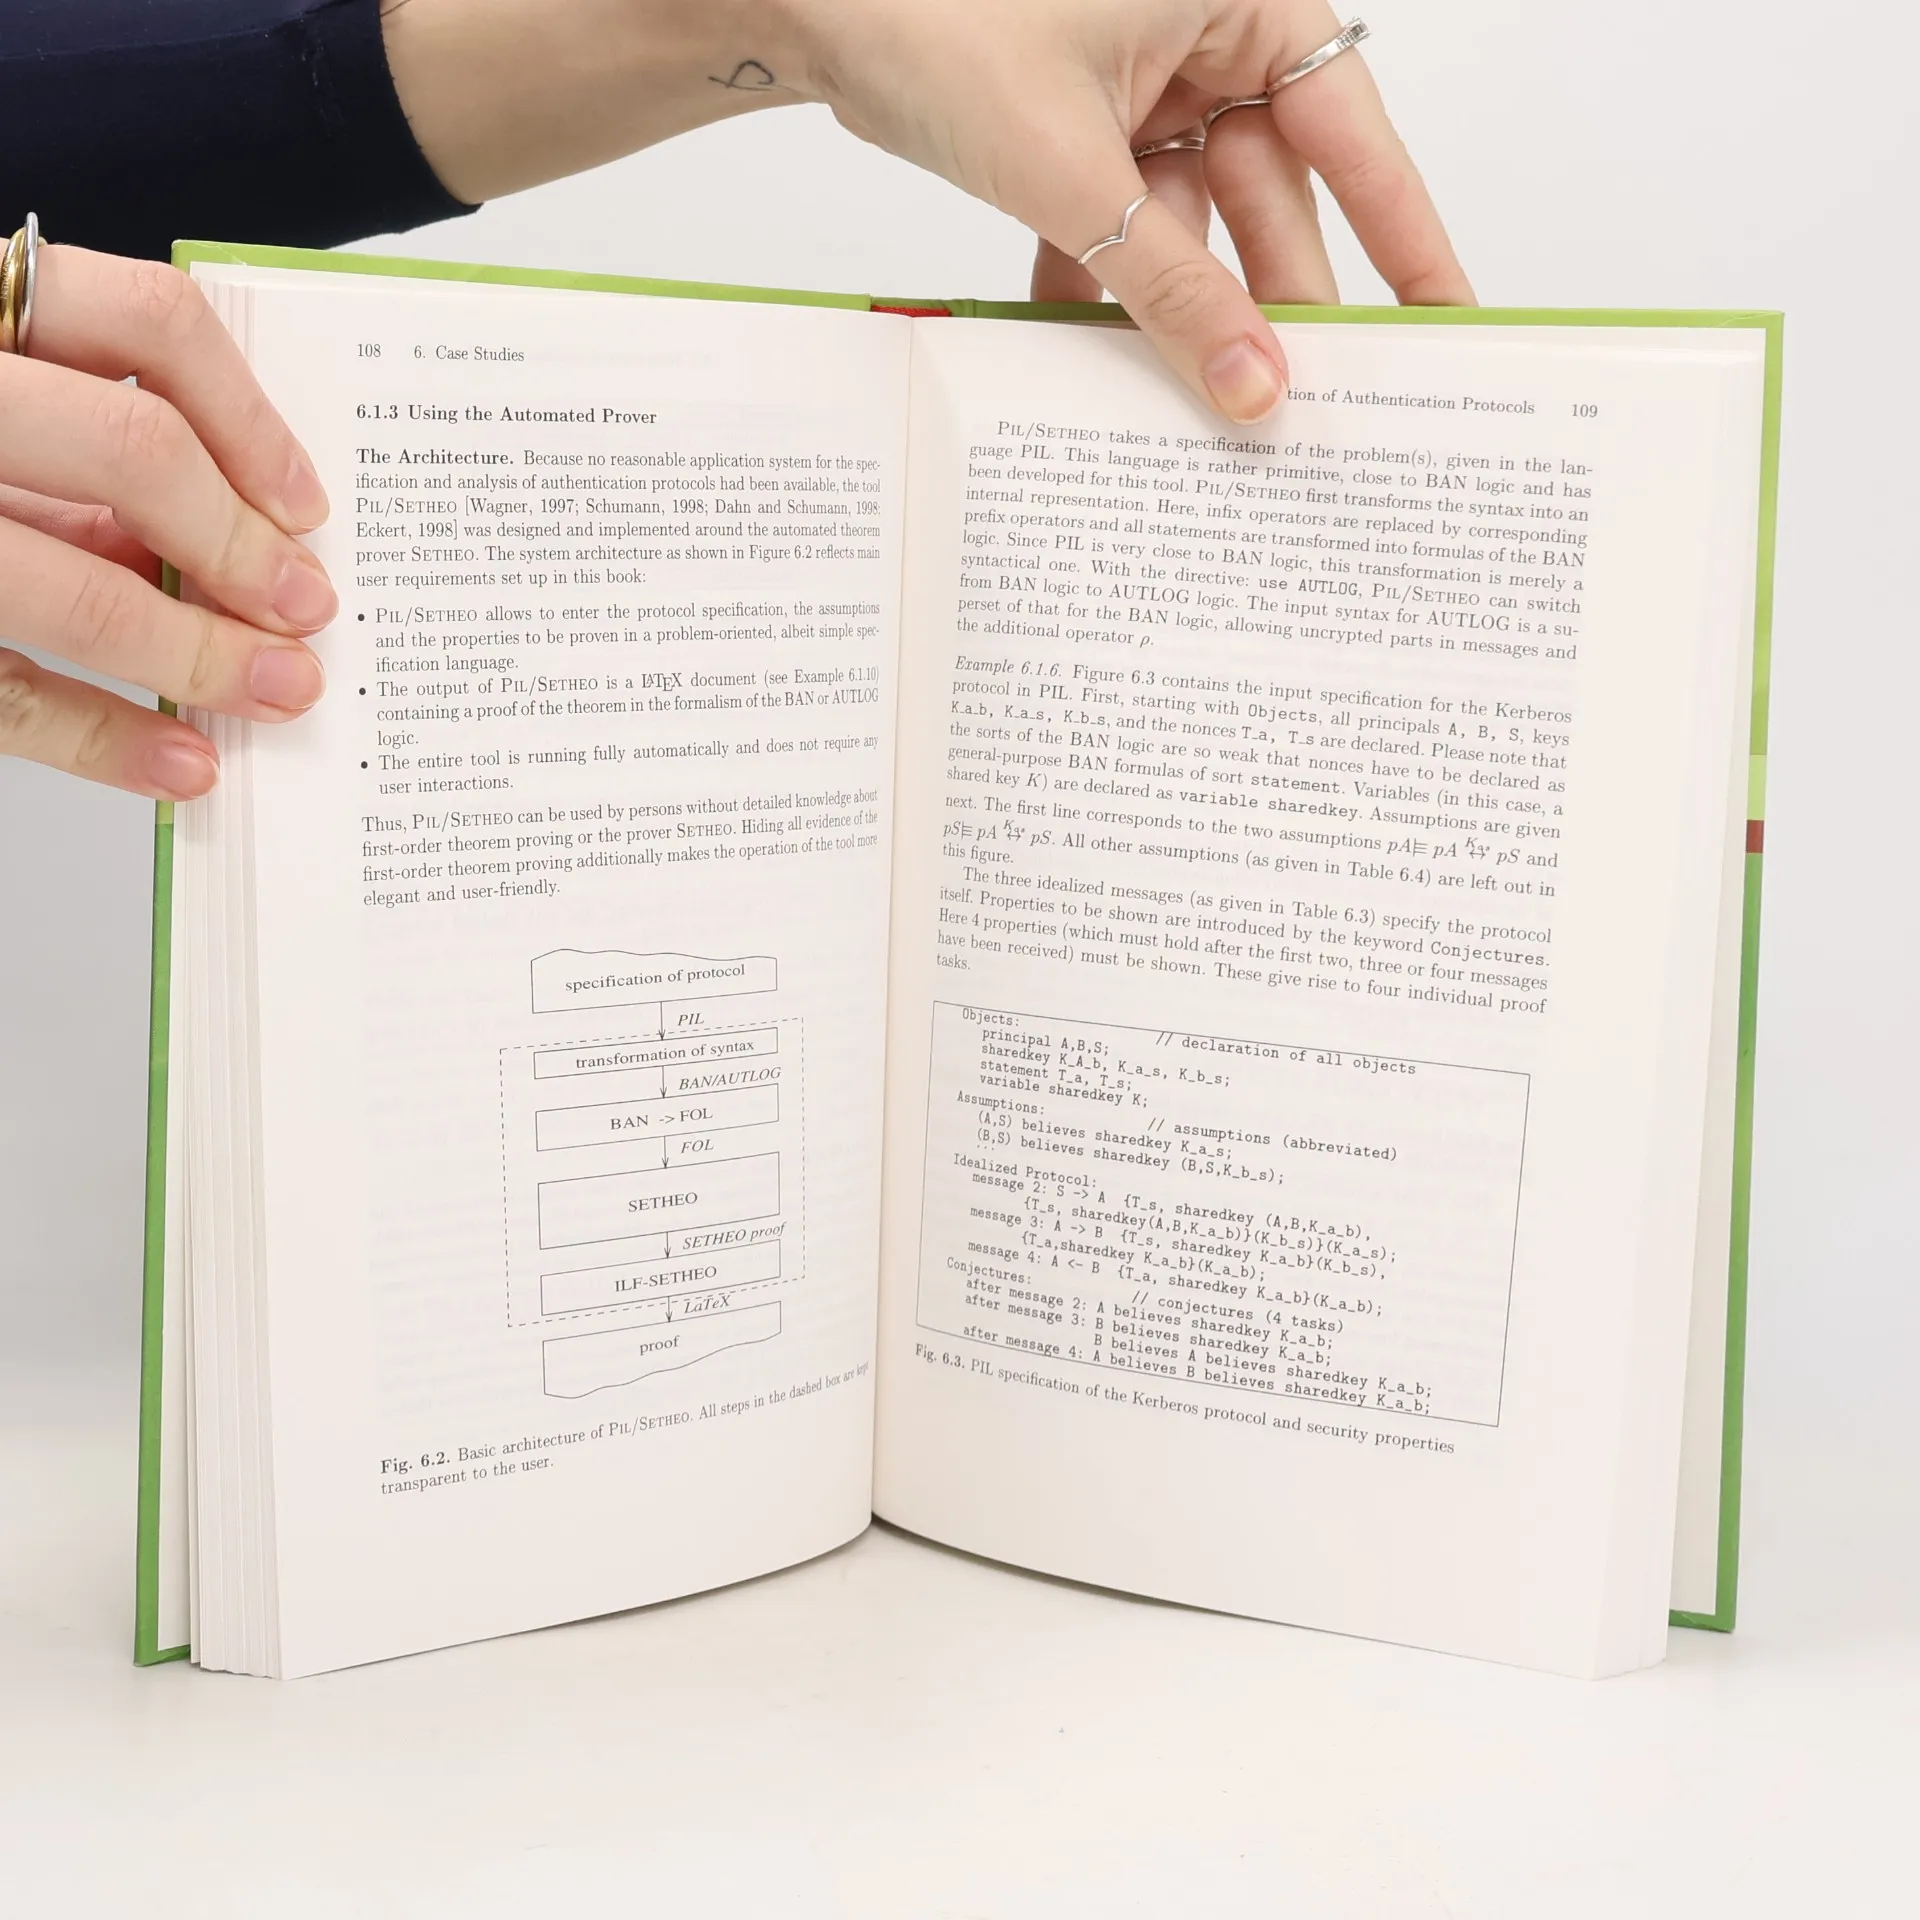
Growing demands for the quality, safety, and security of software can only be satisfied by the rigorous application of formal methods during software design. This book methodically investigates the potential of first-order logic automated theorem provers for applications in software engineering. Illustrated by complete case studies on protocol verification, verification of security protocols, and logic-based software reuse, this book provides techniques for assessing the prover's capabilities and for selecting and developing an appropriate interface architecture.
Nákup knihy
Automated Theorem Proving in Software Engineering, D. Loveland, Johann M. Ph. Schumann
- Jazyk

- Rok vydania
- 2001
- Väzba
- (pevná),
- Stav knihy
- Dobrá
- Cena
- 31,99 €
Doručenie
Platobné metódy
Nikto zatiaľ neohodnotil.
- Titul
- Automated Theorem Proving in Software Engineering
- Jazyk
- anglicky
- Vydavateľ
- Springer
- Rok vydania
- 2001
- Väzba
- pevná
- Počet strán
- 228
- ISBN10
- 3540679898
- ISBN13
- 9783540679899
- Série
- Kategórie
- Štítky
- Architektúra, Západná Európa, Umelá inteligencia, Logika, Operačné systémy, Vývoj softvéru, Informačné systémy
- Anotácia
- Growing demands for the quality, safety, and security of software can only be satisfied by the rigorous application of formal methods during software design. This book methodically investigates the potential of first-order logic automated theorem provers for applications in software engineering. Illustrated by complete case studies on protocol verification, verification of security protocols, and logic-based software reuse, this book provides techniques for assessing the prover's capabilities and for selecting and developing an appropriate interface architecture.